eMudhra breach: India's DSC chain is separate from the 8 blocked certificates
Published · Updated
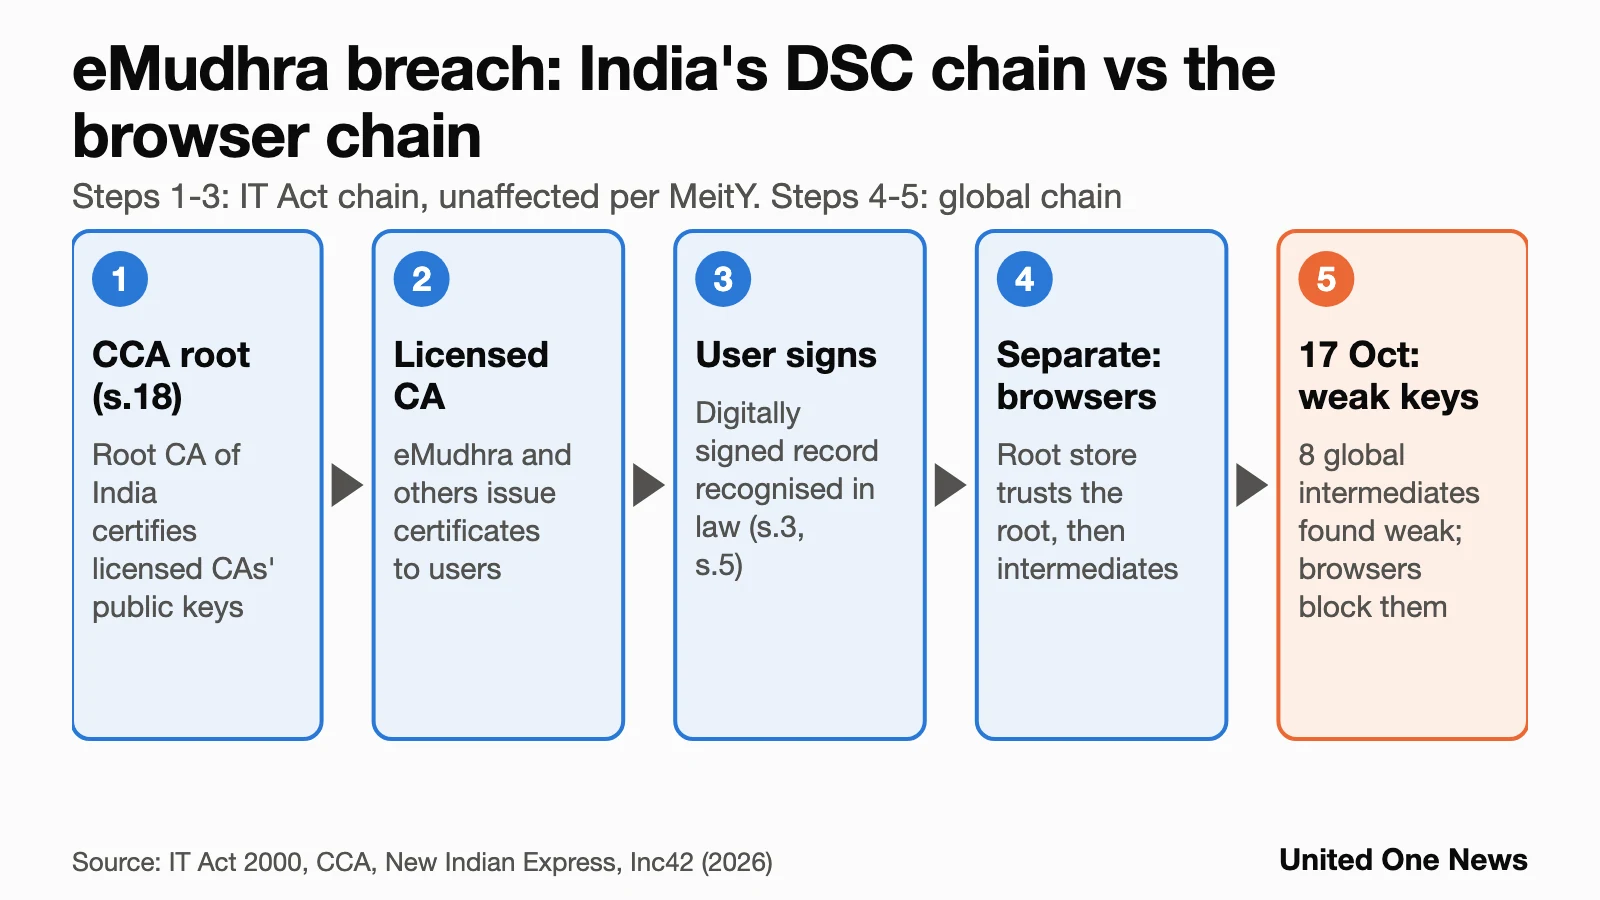
Weak private keys in 8 eMudhra intermediate certificates led Google and Mozilla to block them, but MeitY says Indian DSC and eSign services are unaffected. How the IT Act's chain of trust works, from the CCA's root to a user's signature, and what comes next.
Original report · Explained
Does the eMudhra breach affect Indian digital signature certificates (DSCs)? No, according to the Ministry of Electronics and Information Technology (MeitY), which said on 21 October 2026 that DSC and eSign services are unaffected and that the impact on Indian websites was "very limited and for a very short interval" (The New Indian Express, 2026a). The flaw sits in eMudhra's separate global business: the private keys of 8 intermediate certificate authority (CA) certificates, 6 for TLS (website) certificates and 2 for code signing, were generated with too little randomness, CERT-In's advisory said (The New Indian Express, 2026b).
Keys made that way could be recovered almost instantly, Inc42 reported (Inc42, 2026). eMudhra says only 1 of the 8 was in production and none issued certificates to end users; Google found no certificates from the six TLS intermediates in public Certificate Transparency (CT) logs (The New Indian Express, 2026b; Inc42, 2026).
Mozilla and Google have blocked the six TLS intermediates, and Chrome will remove the emSign ECC Root CA - G3 from its root store from 27 October 2026 (The New Indian Express, 2026b). eMudhra shares fell 20%, hitting the lower circuit at Rs 431.55 on the BSE on 21 October (Inc42, 2026). See how every outlet covered the eMudhra breach.
These notes explain the two chains of trust involved, the IT Act sections behind India's chain, and what a compromised certifying authority means for users.
What it is
A digital signature can be trusted only because a chain of authorities vouches for the key behind it.
- Digital signature: under section 3 of the IT Act 2000, a subscriber authenticates an electronic record using an asymmetric crypto system, which pairs a private key with a public key, and a hash function (Government of India, 2000).
- Certifying Authority (CA): a licensed body that issues certificates to users. eMudhra, based in Bengaluru, was licensed as a CA in 2008 (Inc42, 2026).
- Root CA: the top of a chain. In India, the Root CA of India, set up by the Controller of Certifying Authorities (CCA), certifies the public keys of licensed CAs (CCA, n.d.).
- Intermediate CA: a certificate below a root that can itself issue certificates (Inc42, 2026).
- TLS and code-signing certificates: TLS certificates are used by websites; code-signing certificates are used to sign software.
eMudhra runs two separate chains. The first, its Indian DSC and eSign business, is licensed and regulated by the CCA. The second, its global TLS and code-signing business, is trusted by browsers and audited under WebTrust by BDO International; MeitY is not involved in that audit (The New Indian Express, 2026a). The incident concerns only the second chain (The New Indian Express, 2026b).
Background and timeline
India's chain is 26 years old, and this is not the first time browsers have acted on an Indian certificate problem.
- 2000: the IT Act is passed as Act 21 of 2000; the CCA's office starts on 1 November 2000 (Government of India, 2000; CCA, n.d.).
- 2008: eMudhra is licensed as a CA (Inc42, 2026).
- 2014: the National Informatics Centre (NIC) misissues certificates for Google domains; Google then limits the India CCA root in Chrome to gov.in and nic.in (Inc42, 2026).
- 30 April 2025: at eMudhra's key ceremony, using FIPS 140-2 Level 3 hardware security modules, a flaw creates a second set of weak keys beside the strong ones; the weak keys are published to browser root stores, the company says (The Hindu BusinessLine, 2026).
- 17 October 2026: a researcher, "Wayne", reports the flaw to Apple, Google, Microsoft and Mozilla; Mozilla engineer Dennis Jackson publishes technical details (Inc42, 2026).
- 21 October 2026: eMudhra, CERT-In and MeitY issue statements; MeitY sets up a special team (The Hindu BusinessLine, 2026; The New Indian Express, 2026a).
- 27 October 2026: Chrome starts removing emSign ECC Root CA - G3 (The New Indian Express, 2026b).
What the law says
India's chain of trust is set by the IT Act 2000, from the Controller at the top to the signature on a record.
- Section 3: a subscriber authenticates an electronic record by a digital signature, using an asymmetric crypto system and a hash function.
- Section 5: the law recognises records signed this way.
- Section 17: the Central Government appoints the Controller of Certifying Authorities.
- Section 18: the Controller supervises CAs, certifies their public keys (clause b) and sets standards (clause c). The Root CA of India is set up under section 18(b) (CCA, n.d.).
- Section 21: any person may apply for a licence to be a CA, and must meet qualification, manpower, financial and infrastructure tests.
- Section 30: a CA must use hardware, software and procedures that are secure from intrusion and misuse.
- Section 35: a licensed CA issues certificates to users.
- Section 38(2)(c): a CA may revoke a certificate if its "private key or security system was compromised" (Government of India, 2000).
The browser chain where the weak keys were found is overseen differently: browsers decide whether to trust it, it is audited under WebTrust, and MeitY is not involved in that audit (The New Indian Express, 2026a).
Institutions and the response
Indian regulators and the global browser makers have each acted on their own chain.
- CCA and the Root CA of India: under MeitY; they license and supervise CAs in India's chain (CCA, n.d.).
- CERT-In: issued the 21 October advisory on the 8 intermediates (The New Indian Express, 2026b).
- MeitY special team: set up to examine the incident (The New Indian Express, 2026a).
- Browser root programmes: run by Apple, Google, Microsoft and Mozilla, who were told of the flaw. Mozilla blocked the six TLS intermediates through OneCRL, and Google through CRLSet (The New Indian Express, 2026b; Inc42, 2026).
- BDO International: audits eMudhra's global business under WebTrust (The New Indian Express, 2026a).
The numbers
The affected business is small for eMudhra, but the market reaction was not.
- 8: intermediate CA certificates with weak keys, 6 for TLS and 2 for code signing (CERT-In advisory of 21 October 2026, via The New Indian Express, 2026b).
- 1 of 8: in production, according to eMudhra (Inc42, 2026).
- 0: end-user certificates issued by the 8, eMudhra says; Google found none from the six TLS intermediates in public CT logs (The New Indian Express, 2026b).
- About 1%: the share of eMudhra's revenue from the affected global TLS business, the company said on 21 October (The Hindu BusinessLine, 2026).
- 20%: the fall in eMudhra's shares on 21 October, to the lower circuit of Rs 431.55 on the BSE (Inc42, 2026).
Arguments for and against
The government and the company say the impact is limited; Inc42 asks who watches an Indian CA that also works in global markets.
- MeitY and eMudhra: the global business is separate and small, Indian DSCs are unaffected, and fear-mongering is unwarranted (The New Indian Express, 2026a; The Hindu BusinessLine, 2026).
- The oversight question: Inc42 asks how India oversees licensed CAs that also run global infrastructure, and MeitY is not involved in the global audit (Inc42, 2026; The New Indian Express, 2026a).
- The device question: devices that skip revocation checks may still trust the affected chain (Inc42, 2026).
- The trust question: "Even a relatively small mistake... can affect confidence in the wider industry," said Abhijeet Zilpelwar, CTO of pi-labs (Inc42, 2026).
What happens next
The next date is 27 October, when Chrome starts removing the emSign root.
- CERT-In advises users and organisations to install the latest browser, app and operating system updates, make sure revocation and distrust data reach their systems, and find any services that rely on the affected intermediates or on emSign ECC Root CA - G3 (The New Indian Express, 2026b).
- eMudhra is issuing replacement certificates (Deccan Herald, 2026).
- Still unknown: the root cause beyond the key-generation flaw, and who audited the roots (Inc42, 2026).
Questions people are asking
Is my Indian digital signature (DSC) affected by the eMudhra breach?
MeitY and eMudhra say DSC and eSign services under the CCA are unaffected (The New Indian Express, 2026a).
What is an intermediate CA certificate?
A certificate below a root certificate that can itself issue certificates; 8 of eMudhra's had weak private keys (Inc42, 2026).
Was customer data stolen in the eMudhra breach?
eMudhra ruled out a data breach, The Hindu BusinessLine reported; the problem is weak keys, and eMudhra says none of the 8 issued end-user certificates (The Hindu BusinessLine, 2026; Inc42, 2026).
What should organisations do?
Install the latest browser, app and system updates, and make sure revocation and distrust data reach their systems, CERT-In says (The New Indian Express, 2026b).
For students
GS paper: GS Paper III (cyber security; science and technology).
Key terms
- Certifying Authority (CA): a licensed body that issues digital signature certificates (sections 21 and 35).
- Controller of Certifying Authorities (CCA): appointed by the Central Government to license and supervise CAs (section 17).
- Root CA of India: the top of India's chain, set up under section 18(b).
- Intermediate CA: a certificate below a root that can itself issue certificates.
- Public and private key: the key pair of an asymmetric crypto system.
- TLS certificate: a certificate used by websites.
- Code-signing certificate: a certificate used to sign software.
- Revocation: cancelling a certificate, allowed when its private key is compromised (section 38).
Prelims facts
- The IT Act 2000 is Act 21 of 2000; the CCA's office started on 1 November 2000.
- Section 17: the Central Government appoints the CCA. Section 18(b): the basis of the Root CA of India.
- Section 21 covers licences for CAs; section 38 covers revocation.
- Section 3: a digital signature uses an asymmetric crypto system and a hash function.
- 2014: Chrome limited the India CCA root to gov.in and nic.in after NIC misissued Google certificates.
- 27 October 2026: Chrome starts removing emSign ECC Root CA - G3.
Previous-year questions
- UPSC CSE Prelims 2019 (GS) asked students to judge statements on what a digital signature is: a record identifying the certifying authority, a proof of identity, and a method of signing that ensures the content is unchanged. Answer keys online disagree (statement 3 only, or 2 and 3), so check UPSC's official key (CollectorBabu, n.d.).
- UPSC CSE Mains 2013: "What is a digital signature? What does its authentication mean? Give various salient built-in features of a digital signature." (Superkalam, n.d.)
Mains practice question (250 words)
India's digital signature system rests on a chain of trust created by the IT Act 2000. Explain how this chain works, and, with reference to the eMudhra incident of October 2026, discuss the challenges of overseeing licensed certifying authorities that also operate in global markets.
Prelims practice question
Under the Information Technology Act 2000, who appoints the Controller of Certifying Authorities? (a) CERT-In (b) The Central Government (c) The Reserve Bank of India (d) The Supreme Court
Answer: (b), under section 17.
How we did this
We read the IT Act 2000 as published by PRS Legislative Research, sections 3 to 38, and the CCA's own account of its role, and built the trust-chain flow chart from them. We set the law against statements by eMudhra, CERT-In and MeitY on 21 October 2026, as reported by The Hindu BusinessLine, The New Indian Express and Deccan Herald, and against Inc42's analysis. We did not read CERT-In's advisory or the browser makers' notices directly. The previous-year questions come from CollectorBabu and Superkalam.
References
- The Hindu BusinessLine (2026) eMudhra flags weak keys in eight certificate authorities, rules out data breach. The Hindu BusinessLine. Available at: eMudhra flags weak keys in eight certificate authorities (Accessed: 21 October 2026).
- Deccan Herald (2026) eMudhra discloses compromise of private keys linked to 8 certificates. Deccan Herald. Available at: eMudhra discloses compromise of private keys (Accessed: 21 October 2026).
- The New Indian Express (2026a) Government sets up special team to probe eMudhra security incident; MeitY says Indian impact 'very limited'. The New Indian Express. Available at: Government sets up special team to probe eMudhra security incident (Accessed: 21 October 2026).
- The New Indian Express (2026b) CERT-In warns of security risk in eight eMudhra digital certificates. The New Indian Express. Available at: CERT-In warns of security risk in eight eMudhra digital certificates (Accessed: 21 October 2026).
- Inc42 (2026) eMudhra weak link tests India's chain of digital trust. Inc42. Available at: eMudhra weak link tests India's chain of digital trust (Accessed: 21 October 2026).
- Controller of Certifying Authorities (n.d.) About CCA. Ministry of Electronics and Information Technology. Available at: About CCA (Accessed: 21 October 2026).
- Government of India (2000) The Information Technology Act, 2000 (Act 21 of 2000), as amended. PRS Legislative Research. Available at: The Information Technology Act, 2000 (Accessed: 21 October 2026).
- CollectorBabu (n.d.) UPSC IAS 2019: Consider the following statements: a digital signature is... CollectorBabu. Available at: UPSC IAS 2019: a digital signature is (Accessed: 21 October 2026).
- Superkalam (n.d.) UPSC Mains 2013: What is a digital signature? Superkalam. Available at: UPSC Mains 2013: What is a digital signature (Accessed: 21 October 2026).
This story was produced, reviewed, edited and verified by the reporter before publication, with AI assistance where required.
Covered by 31 outlets across the spectrum: 23% left, 58% center, 16% right.
Who is covering this story
- Left-leaning (5): The Hindu, Superkalam (summary of Indian Express report), The New Indian Express, The Federal, NDTV
- Center (11): Bleepingcomputer, Free Press Journal, YourStory, Business Today, Hindustan Times, Inc42, CCA, PRS Legislative Research, Deccan Herald, The Hindu BusinessLine, Mid-Day
- Right-leaning (4): Times Now, Sunday Guardian, Times of India, OpIndia
- Not yet rated (1): CollectorBabu
Sources
- Mozilla, Google, Apple block compromised eMudhra CA certificates — Bleepingcomputer (center, AI-estimated) ·
- Apple, Google Block Security Certificates Issued By Indian Firm eMudhra: What Happened? — Times Now (right-leaning) ·
- Eight web security keys of firm used by Govt. and PSUs leaked — The Hindu (left-leaning) ·
- eMudhra Shares Crash 20% After Security Researcher Flags Weak Encryption Keys In Eight TLS Certificates — Free Press Journal (center) ·
- eMudhra Security Scare: Why Google, Apple and Microsoft Blocked Eight Digital Certificates? Check What Happened, Security Risks & What Users Need to Know — Sunday Guardian (right-leaning) ·
- eMudhra faces scrutiny after weak certificate keys raise web security concerns — YourStory (center) ·
- Why Did Apple, Google, Microsoft, & Mozilla Block Certificates From Indian Firm eMudhra? — Free Press Journal (center) ·
- Major security flaw triggers action from Google and Apple against eMudhra certificates — Business Today (center) ·
- eMudhra security breach: What it means for smartphone, internet users — Times of India (right-leaning) ·
- 'Impact has been very limited': MeitY on eMudhra security incident, says Indian DSC and eSign unaffected — Business Today (center) ·
- Centre orders probe as Indian firm's key-making error leaves holes in web security — Hindustan Times (center) ·
- eMudhra Weak Link Tests India’s Chain Of Digital Trust — Inc42 (center) ·
- Article from CCA — CCA (center) ·
- UPSC IAS 2019: Consider the following statements: A digital signa... | CollectorBabu — CollectorBabu (not yet rated) ·
- Article from PRS Legislative Research — PRS Legislative Research (center) ·
- What is a digital signature? What does its authentication mean? Giver various salient built-in features of a digital signature. | UPSC Mains 2013 GS 3 Model Answer — Superkalam (summary of Indian Express report) (left-leaning) ·
- eMudhra private key breach limited to global TLS operations, MeitY says — Deccan Herald (center) ·
- CERT-In warns of security risk in eight eMudhra digital certificates — The New Indian Express (left-leaning) ·
- Government sets up special team to probe eMudhra security incident; MeitY says Indian impact ‘very limited’ — The New Indian Express (left-leaning) ·
- eMudhra flags weak keys in eight certificate authorities, rules out data breach — The Hindu BusinessLine (center) ·
- Explained: What is the eMudhra certificate compromise about and should you be worried? — The Federal (left-leaning) ·
- eMudhra Cybersecurity Issue: Weak Encryption Keys Raise Web Security Concerns — Times Now (right-leaning) ·
- Cybersecurity alert: eMudhra reports compromise of eight CA inter certificates — Mid-Day (center) ·
- ‘Limited impact on Indian websites, applications’: MeitY clarifies after eMudhra security scare; all you need to know about the issue that rattled Google, Apple and others — OpIndia (right-leaning) ·
- eMudhra Exits Global Website Security Business After Weak Keys Found In Eight Certificates — NDTV (left-leaning) ·
- eMudhra security breach explained: How weak cryptographic keys can be a threat — Mid-Day (center) ·
- eMudhra to exit global website security certificate business — YourStory (center) ·
- eMudhra To Exit Certificate Business As Security Flaw Triggers Distrust — Inc42 (center) ·
- How a flaw in eMudhra’s digital keys raised concerns over internet security — The New Indian Express (left-leaning) ·
- BT BIG STORY: What happens when the keys to internet security are no longer secret — Business Today (center) ·
- eMudhra shuts global website certificate business after key flaws exposed, calls scrutiny ‘disproportionate’ — Hindustan Times (center) ·