SBI data breach: what happens next under the DPDP Act and CERT-In rules
Published · Updated
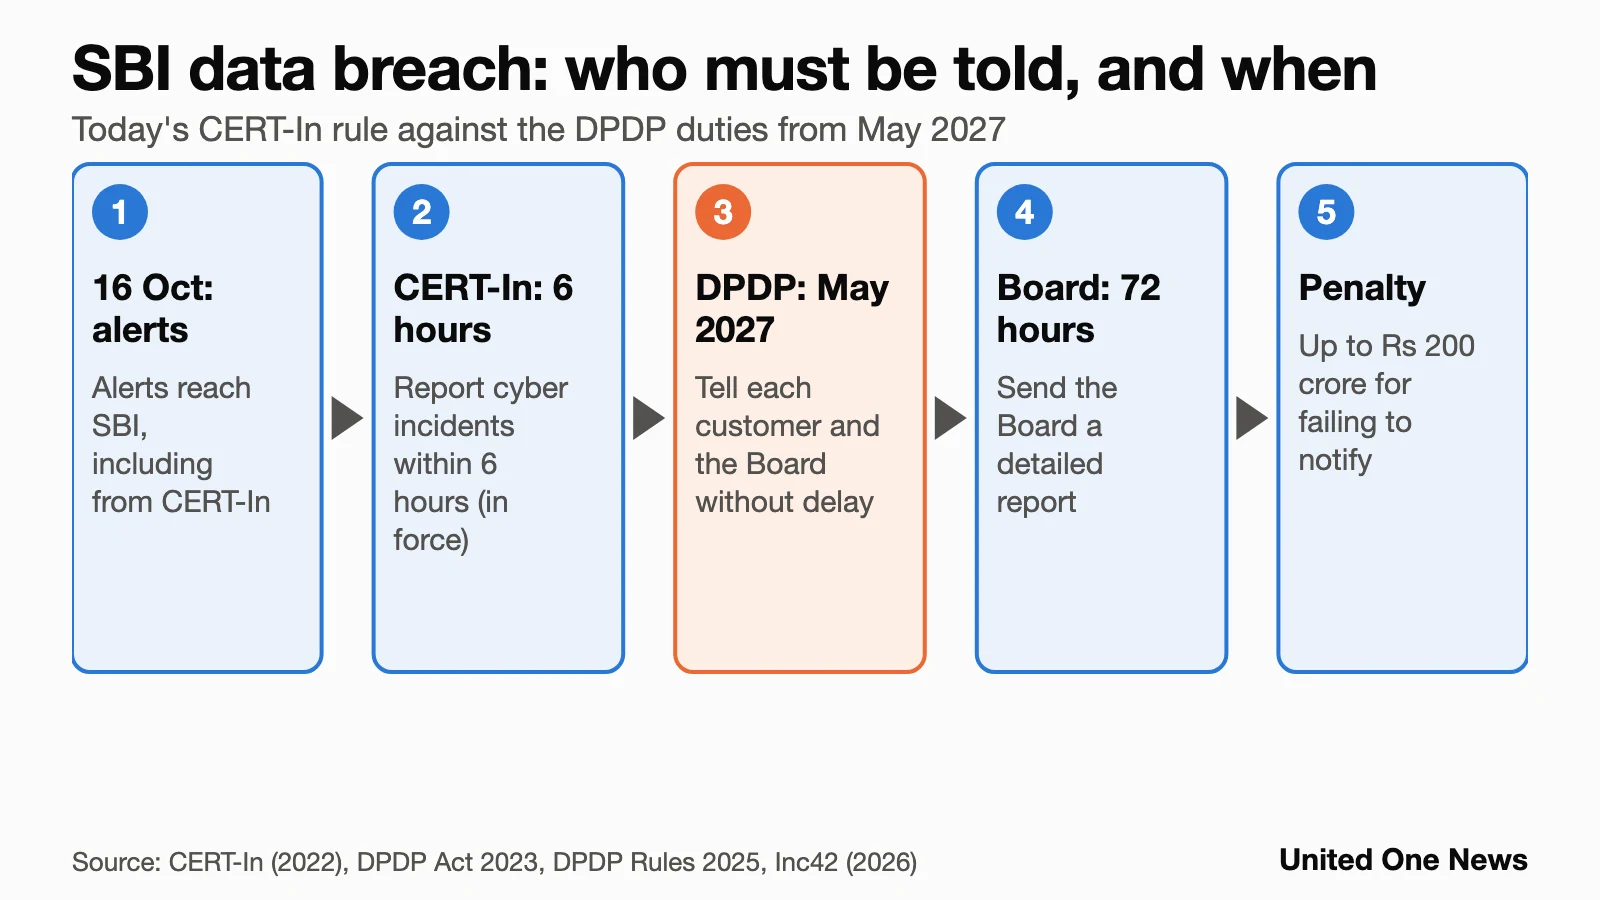
SBI says 3,897 customer records are among 3.75 lakh rows found on the dark web, and it has published no lookup tool. The DPDP rule that makes a bank tell each affected customer starts only in May 2027. What applies today, and what customers can do.
Original report · Explained
Can SBI customers check whether their details were leaked in the SBI data breach? Not yet: in the reports we read, the State Bank of India (SBI) had published no lookup tool by 21 October 2026, the day it told stock exchanges that 3,897 customer records with personal information were among about 3.75 lakh records found on the dark web (ABP Live, 2026; Inc42, 2026). What happens next under the Digital Personal Data Protection (DPDP) Act is further off: the rule that makes a bank tell each affected customer starts only around 14 May 2027 (MeitY, 2025; Shardul Amarchand Mangaldas, 2025).
The exposed fields include mobile numbers, dates of birth, names, gender, email and postal addresses, branch and CIF identifiers, lead IDs and loan metadata, ABP Live reported (ABP Live, 2026). SBI said alerts reached it on 16 October from its threat-intelligence provider, the Defence Cyber Agency and CERT-In, and that core banking is unaffected (Inc42, 2026).
A group calling itself "Siriusim" claimed 3.75 lakh rows plus 2,722 PDFs of loan applications and account-opening forms; Inc42 could not verify the claim (Inc42, 2026). Congress media head Pawan Khera said on 21 October: "SBI did not even detect the breach itself" (The New Indian Express, 2026). See how every outlet covered the SBI data breach.
These notes set the incident against the rules that apply today, from CERT-In and the Reserve Bank of India (RBI), and the DPDP duties still to come.
What it is
The DPDP Act defines a personal data breach as unauthorised processing, or accidental disclosure, loss of access and similar events, that compromises the confidentiality, integrity or availability of personal data (MeitY, 2023). That is section 2(u).
- Data fiduciary: the organisation that holds the data and owes the duties; here, the bank.
- Data principal: the person the data is about; here, the customer.
- Data Protection Board: the body that receives breach reports and can impose penalties (MeitY, 2023).
Until the DPDP breach clauses start, two older rulebooks do the work: CERT-In's 2022 directions on reporting cyber incidents, and RBI's 2017 rules on what a customer loses when money is taken without permission.
Background and timeline
India's breach rules have built up since 2017, and the main customer-notice duty has still not started.
- 6 July 2017: RBI limits customer liability in unauthorised electronic banking transactions (RBI, 2017).
- 2017: the Supreme Court, in Puttaswamy v Union of India, places the right to privacy within Article 21 (Anantam IAS, n.d.).
- 28 April 2022: CERT-In issues directions under section 70B(6) of the IT Act (CERT-In, 2022).
- August 2023: the DPDP Act is published as Act 22 of 2023 (MeitY, 2023).
- 13 November 2025: the DPDP Rules are gazetted as G.S.R. 846(E) (MeitY, 2025).
- 16 October 2026: alerts about the leak reach SBI (Inc42, 2026).
- 21 October 2026: SBI's exchange filing; Congress demands accountability (ABP Live, 2026; The New Indian Express, 2026).
- About 14 May 2027: breach intimation, penalties and the repeal of IT Act section 43A start, 18 months after the Rules were gazetted (Shardul Amarchand Mangaldas, 2025).
What the law says
Today a breach must be reported to CERT-In within 6 hours; the DPDP duty to tell each customer starts only in 2027.
CERT-In directions, 28 April 2022 (in force)
- Cyber incidents must be reported to CERT-In within 6 hours of noticing them; "Data Breach" and "Data Leak" are listed incident types (CERT-In, 2022).
- Logs must be kept for 180 days.
- The directions are issued under IT Act section 70B(6); failing to comply invites action under section 70B(7).
RBI customer protection rules, 6 July 2017 (in force)
- A customer who tells the bank about an unauthorised transaction within 3 working days has zero liability, and the bank must credit the amount within 10 working days (RBI, 2017).
DPDP Act 2023 (breach clauses not yet in force)
- Section 8(5): the data fiduciary must take reasonable security safeguards.
- Section 8(6): after a breach, it must tell the Board and "each affected Data Principal" (MeitY, 2023).
- Section 44(2)(a): IT Act section 43A is omitted once this provision starts.
- Schedule: up to Rs 250 crore for failing to keep reasonable safeguards, and up to Rs 200 crore for failing to notify a breach.
DPDP Rules 2025
- Rule 6: safeguards include encryption, access control and logs.
- Rule 7(1): tell each affected person, in plain language and "without delay", what happened, the likely consequences, the steps taken, the safety steps they can take, and a contact (MeitY, 2025).
- Rule 7(2): tell the Board without delay, then send a detailed report within 72 hours.
- Rule 1(4): these provisions start 18 months after the Rules were published.
Institutions, committees and judgments
Five bodies matter here, and one judgment underpins the whole law.
- Data Protection Board: four members, based in the National Capital Region, per Shardul Amarchand Mangaldas; it will receive breach reports and impose penalties (Shardul Amarchand Mangaldas, 2025).
- CERT-In: issued the 2022 directions and was one of the agencies that alerted SBI (CERT-In, 2022; Inc42, 2026).
- Defence Cyber Agency: also alerted SBI (Inc42, 2026).
- RBI: sets banks' customer-liability rules (RBI, 2017).
- A CERT-In-empanelled auditor: SBI has engaged an independent one to establish the data's authenticity, source and extent (ABP Live, 2026).
- Puttaswamy v Union of India (2017): the Supreme Court judgment that put privacy within the right to life under Article 21 (Anantam IAS, n.d.).
The numbers
About 1 in 100 of the records examined so far is a customer record with personal details.
- 3,897: customer records with personal information, out of about 3.75 lakh (375,000) records examined, per SBI's 21 October 2026 filing (ABP Live, 2026). That is about 1%: 3,897 divided by 375,000.
- 2,722: PDFs "Siriusim" claims to hold, unverified (Inc42, 2026).
- 6 hours and 180 days: CERT-In's reporting deadline and log period, since 28 April 2022 (CERT-In, 2022).
- 72 hours: the deadline for a detailed report to the Board under DPDP Rule 7(2)(b) (MeitY, 2025).
- Rs 250 crore and Rs 200 crore: the maximum DPDP penalties for weak safeguards and for failing to notify. Other caps in the Schedule are Rs 200 crore (children's data), Rs 150 crore (significant data fiduciaries) and Rs 50 crore (any other breach of the Act) (MeitY, 2023).
- 3 and 10 working days: RBI's limits for a customer to report fraud and for a bank to credit the money (RBI, 2017).
Arguments for and against
SBI says the damage is contained; Congress says SBI was slow; lawyers note the coming rule has no size threshold.
- SBI's position: operations are normal, core banking is unaffected, and an outside CERT-In-empanelled agency is checking the data (Inc42, 2026; ABP Live, 2026).
- Congress's position: Khera said SBI learned of the breach from others and had not yet informed affected customers (The New Indian Express, 2026).
- The legal view: DPDP reporting applies "regardless of the impact or materiality" of a breach, Shardul Amarchand Mangaldas wrote (Shardul Amarchand Mangaldas, 2025). On that reading, the size of a breach does not decide whether notices are due once Rule 7 is in force.
What happens next
The audit comes first, the DPDP duties in 2027.
- The independent audit will establish whether the data is genuine, where it came from and how far it reaches (ABP Live, 2026).
- Around 14 May 2027, breach intimation, penalties and the repeal of IT Act section 43A take effect (Shardul Amarchand Mangaldas, 2025).
- For customers, RBI's framework points to two steps: register for SMS alerts, and report any unauthorised transaction quickly (RBI, 2017).
Still unknown: whether SBI has told affected customers or will offer a lookup tool, and whether the 3.75 lakh rows are genuine (Inc42, 2026).
Questions people are asking
How do I check if my SBI data was leaked?
SBI had published no lookup tool in the reports we read. It has identified 3,897 customer records and its audit continues (ABP Live, 2026).
Does the DPDP Act force SBI to tell me?
Not yet. DPDP Rule 7, which requires notice to each affected person, starts around May 2027 (MeitY, 2025; Shardul Amarchand Mangaldas, 2025).
What if money is taken from my account?
Tell the bank within 3 working days for zero liability under RBI's 2017 rules; the bank must credit the amount within 10 working days (RBI, 2017).
What is CERT-In's 6-hour rule?
Since 28 April 2022, cyber incidents, including data breaches and leaks, must be reported to CERT-In within 6 hours of being noticed (CERT-In, 2022).
For students
GS paper: GS Paper III (cyber security, banking) and GS Paper II (right to privacy, governance).
Key terms
- Data fiduciary: the entity that holds personal data and owes duties under the DPDP Act; here, the bank.
- Data principal: the person the data relates to; here, the customer.
- Personal data breach: unauthorised processing, disclosure or loss of access that compromises data (section 2(u)).
- Data Protection Board: the four-member body that will receive breach reports and impose penalties.
- CERT-In: the agency to which cyber incidents must be reported within 6 hours.
- Zero liability: RBI's protection for a customer who reports an unauthorised transaction within 3 working days.
- Reasonable security safeguards: the section 8(5) duty; Rule 6 names encryption, access control and logs.
Prelims facts
- The DPDP Act is Act 22 of 2023; its maximum penalty is Rs 250 crore.
- The DPDP Rules, G.S.R. 846(E), were gazetted on 13 November 2025; Rule 7 sets a 72-hour detailed report to the Board.
- Rule 1(4): the breach provisions start 18 months after publication.
- CERT-In directions, 28 April 2022: 6-hour reporting and 180-day logs.
- RBI, 6 July 2017: zero liability if fraud is reported within 3 working days.
- Puttaswamy (2017) placed privacy within Article 21.
Previous-year question: UPSC CSE Prelims 2018 (GS) began "Right to Privacy is protected as an intrinsic part of Right to Life and Personal Liberty" and asked which part of the Constitution implies this. The answer: Article 21 and the freedoms guaranteed in Part III (Anantam IAS, n.d.).
Mains practice question (250 words)
The DPDP Act 2023 promises every data principal notice of a personal data breach, but the duty begins only in 2027. With reference to the SBI data breach of October 2026, examine how far CERT-In's directions and RBI's rules protect bank customers in the meantime, and suggest improvements.
Prelims practice question
Under CERT-In's directions of 28 April 2022, within how many hours of noticing a cyber incident must it be reported to CERT-In? (a) 6 (b) 24 (c) 48 (d) 72
Answer: (a) 6 hours. 72 hours is the DPDP Rules' deadline for a detailed report to the Data Protection Board.
How we did this
We read the primary texts: the DPDP Act 2023, the DPDP Rules 2025, CERT-In's 2022 directions and RBI's 2017 customer-protection circular, with Shardul Amarchand Mangaldas's note on when the Rules start. We set them against SBI's 21 October 2026 filing as reported by Inc42 and ABP Live, and the Congress statement in The New Indian Express. We could not verify the 3.75 lakh rows or the 2,722 PDFs, and we found no SBI lookup tool. The timeline, the flow chart and the comparison of the rules are our own.
References
- ABP Live (2026) SBI Data Leak: Is Your Information Safe? Bank Flags 3,897 Exposed Records. ABP Live. Available at: SBI Data Leak: Is Your Information Safe? (Accessed: 21 October 2026).
- Inc42 (2026) SBI Flags Exposure Of 3,897 Customer Records On Dark Web. Inc42. Available at: SBI Flags Exposure Of 3,897 Customer Records On Dark Web (Accessed: 21 October 2026).
- The New Indian Express (2026) SBI owes customers answers; those responsible must be held accountable: Congress on data breach. The New Indian Express. Available at: SBI owes customers answers (Accessed: 21 October 2026).
- MeitY (2023) The Digital Personal Data Protection Act, 2023. Ministry of Law and Justice, Government of India. Available at: The Digital Personal Data Protection Act, 2023 (Accessed: 21 October 2026).
- MeitY (2025) Digital Personal Data Protection Rules, 2025, G.S.R. 846(E). Gazette of India. Available at: Digital Personal Data Protection Rules, 2025 (Accessed: 21 October 2026).
- CERT-In (2022) Directions under section 70B(6) of the IT Act, No. 20(3)/2022-CERT-In. MeitY. Available at: CERT-In Directions, 28 April 2022 (Accessed: 21 October 2026).
- RBI (2017) Customer Protection: Limiting Liability of Customers in Unauthorised Electronic Banking Transactions. Reserve Bank of India. Available at: Customer Protection: Limiting Liability of Customers (Accessed: 21 October 2026).
- Shardul Amarchand Mangaldas (2025) Enforcement of the DPDP Act and notification of the DPDP rules. Shardul Amarchand Mangaldas & Co. Available at: Enforcement of the DPDP Act and notification of the DPDP rules (Accessed: 21 October 2026).
- Anantam IAS (n.d.) UPSC Prelims 2018 GS Question 42: Right to Privacy. Anantam IAS. Available at: UPSC Prelims 2018 GS Question 42 (Accessed: 21 October 2026).
This story was produced, reviewed, edited and verified by the reporter before publication, with AI assistance where required.
Covered by 28 outlets across the spectrum: 25% left, 43% center, 14% right.
Who is covering this story
- Left-leaning (4): The New Indian Express, Scroll.in, Greater Kashmir, The Hindu
- Center (9): Mint, Tribune India, Deccan Herald, Anantam IAS, Inc42, Economic Times, The Hindu BusinessLine, Bollywood Hungama, Gadgets 360
- Right-leaning (3): Times of India, Times Now, Deccan Chronicle
- Not yet rated (4): Shardul Amarchand Mangaldas, CERT-In, MeitY, RBI
Sources
- SBI data leak: Nearly 4,000 customer records found on dark web; what we know so far — Times of India (right-leaning) ·
- SBI probes suspected dark web exposure of 3,897 customer records; no impact on business continuity — The New Indian Express (left-leaning) ·
- Personal details of nearly 3,900 SBI customers leaked on dark web in cyberattack — Scroll.in (left-leaning) ·
- SBI probes suspected dark web exposure of 3,897 customer records, no impact on business continuity — Greater Kashmir (left-leaning, AI-estimated) ·
- SBI data leak raises fraud risks as bank probes exposure of customer records — Mint (center) ·
- 3,897 customer details found on dark web: SBI flags data breach — Tribune India (center) ·
- Cyberattack hits SBI; nearly 4k customers’ data leaked to dark web — Deccan Herald (center) ·
- Enforcement of the DPDP Act and notification of the DPDP rules - Shardul Amarchand Mangaldas & Co — Shardul Amarchand Mangaldas (not yet rated) ·
- CERT In Directions 70B 28.04.2022.pdf — CERT-In (not yet rated) ·
- Right to Privacy is protected as an intrinsic part of Right to Life and… - Anantam IAS — Anantam IAS (center) ·
- SBI Flags Exposure Of 3,897 Customer Records On Dark Web — Inc42 (center) ·
- Article from MeitY — MeitY (not yet rated) ·
- Article from MeitY — MeitY (not yet rated) ·
- SBI owes customers answers; those responsible must be held accountable: Congress on data breach — The New Indian Express (left-leaning) ·
- Notifications | Official Website of Reserve Bank of India — RBI (not yet rated) ·
- SBI confirms data leak, says 4,000 customer records identified on dark web — Times of India (right-leaning) ·
- Cybersecurity experts flag audit gaps after SBI leak, eMudhra breach — Deccan Herald (center) ·
- SBI data leak a matter of grave concern: CPI(M) MP A.A. Rahim — The Hindu (left-leaning) ·
- Don't fall prey to cyber frauds! Searching for bank customer care numbers? Warning from SBI - here’s how to stay safe — Mint (center) ·
- SBI customer data leak scare: Is your money safe? — Economic Times (center) ·
- SBI Cyber Incident: 'Bank Has Individually Informed All Customers Whose Data Was Involved' — Times Now (right-leaning) ·
- Data leak incident: SBI says customer balances completely safe — The Hindu BusinessLine (center) ·
- SBI says it informed customers after details of nearly 3,900 account holders leaked in cyberattack — Scroll.in (left-leaning) ·
- SBI data leak: This is what India's largest public sector bank told customers as 3,897 records flagged in cyber incident — Mint (center) ·
- Road Ministry seeks forensic audit of its portals after vehicle data leak — The Hindu (left-leaning) ·
- CBFC Data Leak: Unreleased Scripts And Film Contracts Exposed? — Deccan Chronicle (right-leaning) ·
- CBFC faces reported data security scare as confidential documents linked to over 500 films are allegedly exposed — Bollywood Hungama (center) ·
- Coinbase, Bithumb and South Korean Financial Firms Report Data Leaks — Gadgets 360 (center) ·