PHP2Shell vulnerability fix: the PHP 8.5.12 update, and none for 8.1
Published · Updated
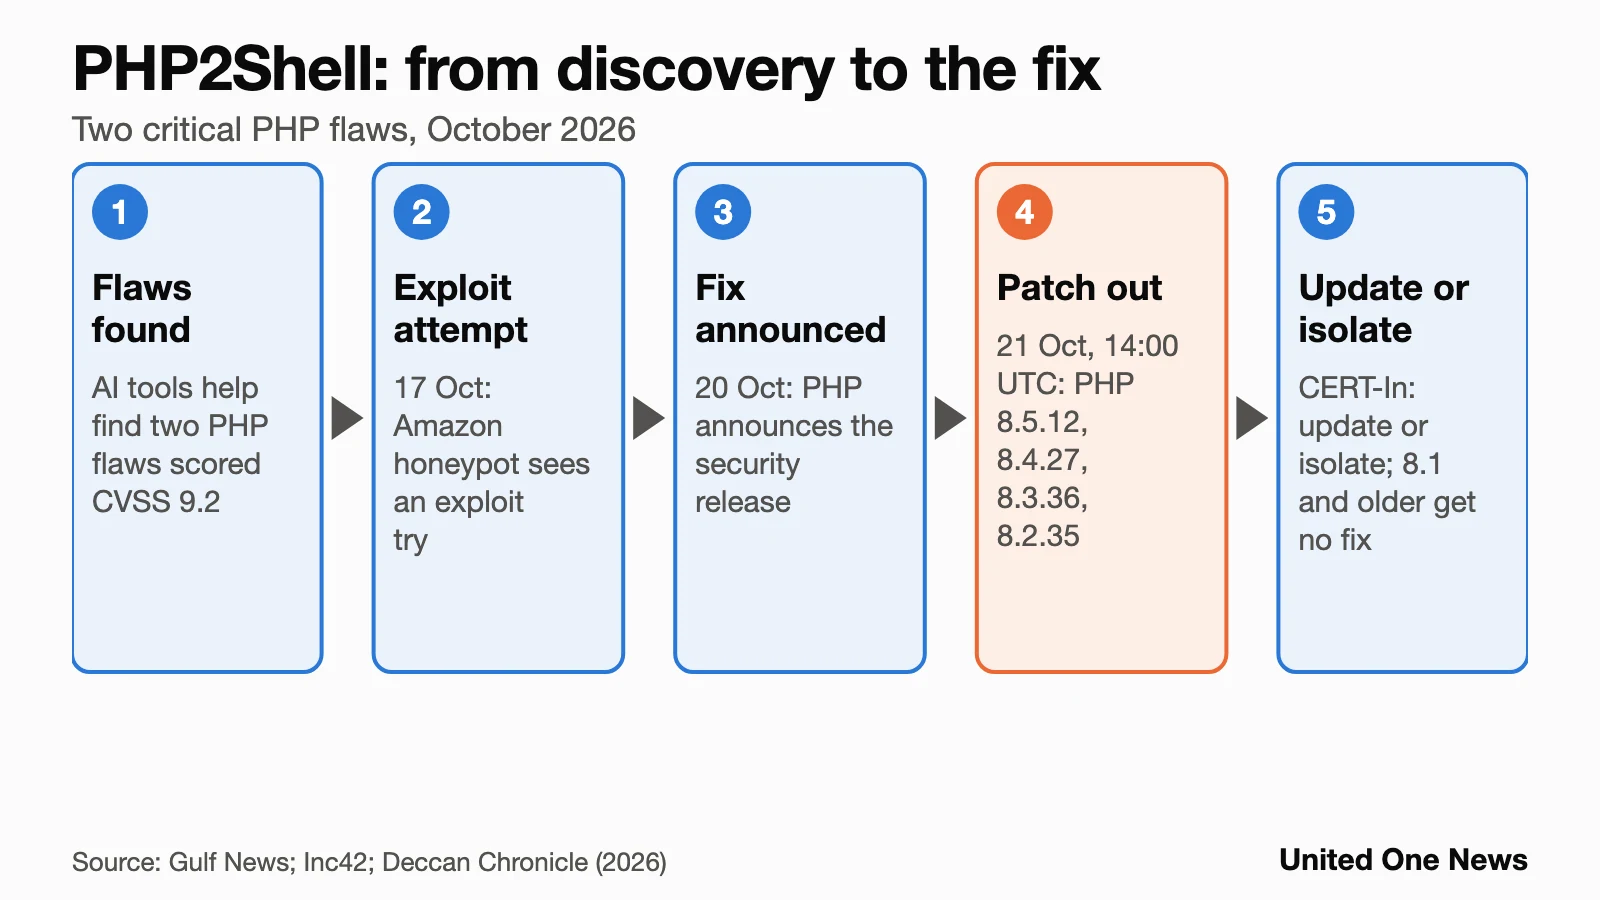
Two critical PHP flaws found with AI help pushed European government sites offline. The fix is out for four PHP versions, but sites on PHP 8.1 or older get no direct update. What to install, and what CERT-In advises.
Original report · Explained
The PHP2Shell vulnerability fix is a PHP update. PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, released at 14:00 UTC on 21 October 2026, close two critical flaws, Gulf News reported; PHP 8.1 and older get no direct update, though some vendors may backport the fix (Gulf News, 2026).
The flaws, CVE-2026-109618 and CVE-2026-109619, both score 9.2 on the CVSS v4 scale. According to the UK's National Cyber Security Centre, they may cause memory corruption and let an attacker run code on a server without logging in (Gulf News, 2026). Inc42 reports they are believed to exist in every PHP version since PHP 5, released in 2004 (Inc42, 2026).
That is why government websites in Finland, the Netherlands, France and Denmark went offline as a precaution (The Irish Times, 2026; Deccan Chronicle, 2026). Which Indian government sites, if any, went offline is not stated in any report we read. See how every outlet covered it.
The PHP 8.5.12 update is the complete fix
"Applying the security update remains the complete solution," the PHP security team said (Gulf News, 2026). What that means by version:
- PHP 8.5, 8.4, 8.3 or 8.2: update to 8.5.12, 8.4.27, 8.3.36 or 8.2.35.
- PHP 8.1 or older: no direct update; only some vendors may backport the fix (Gulf News, 2026; Inc42, 2026).
- Servers running PHP as mod_php face the highest risk (Inc42, 2026).
A WordPress or any other site on an affected PHP version is exposed, and its owner should update PHP through the host, Inc42 says (Inc42, 2026).
Where updating is not possible, agencies advise a blunter step.
Agencies say isolate what cannot be patched
CERT-In, India's cyber-security agency, and the US NSA advised updating or isolating affected systems, Inc42 reported; we could not open CERT-In's advisory itself (Inc42, 2026). The EU's CERT advised isolating internet-facing apps until a fix is verified, and the NSA advised taking systems that cannot be patched offline (The Irish Times, 2026; Gulf News, 2026).
CERT-In also flagged a separate certificate problem this week, explained in eMudhra breach: India's DSC chain is separate from the 8 blocked certificates.
The urgency comes from how much of the web runs on PHP.
PHP runs most of the web
Up to 70% of the internet is supported by PHP, The Irish Times reported on 21 October (The Irish Times, 2026). W3Techs counts about 75% of identifiable websites on PHP, and Censys found 1.5 million of 2.6 million hosts on unfixed PHP versions, Deccan Chronicle reported; neither figure is dated (Deccan Chronicle, 2026). That is about 58% of the hosts Censys counted (1.5 ÷ 2.6).
"This issue impacts the majority of the internet," said Tiffany Farriss of the Drupal Association (Deccan Chronicle, 2026).
How flaws this old stayed hidden is the other half of the story.
AI tools found flaws that hid for years
AI tools helped find flaws that had gone unnoticed for years, and OpenAI says it led a coalition of researchers (The Irish Times, 2026; Deccan Chronicle, 2026). Amazon spotted an attempt to exploit them on a honeypot, a decoy server, on 17 October, before the patch was out (Deccan Chronicle, 2026).
Experts expect intrusions as attackers race to exploit the now-public fixes. "The vulnerabilities are of a very high severity," said cybersecurity expert Brian Honan (The Irish Times, 2026).
How the coverage split
The Irish Times led on scale, the 70% of the internet. Gulf News led on the two patches, Deccan Chronicle on government sites going dark, and Inc42 on the technical detail and the PHP2Shell name (The Irish Times, 2026; Gulf News, 2026; Deccan Chronicle, 2026; Inc42, 2026). None of the reports we read named an Indian site that went offline or quoted the CERT-In advisory's text.
What we don't know yet
- Which Indian sites, if any, were affected, and the date and text of CERT-In's advisory.
- Whether mass exploitation has started in India.
- When the sites taken offline will return; they stay down until patched, with no dated timeline (Deccan Chronicle, 2026).
Questions people are asking
What is the PHP2Shell vulnerability?
Two critical PHP flaws, scored 9.2 on CVSS v4, that can let an attacker run code on a server without logging in (Gulf News, 2026; Inc42, 2026).
Which PHP versions are safe?
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. PHP 8.1 and older get no direct fix (Gulf News, 2026).
Is a WordPress site affected?
Any site on an affected PHP version is exposed; update PHP through the host (Inc42, 2026).
What does CERT-In advise?
Update or isolate affected systems (Inc42, 2026).
Why did government websites go offline?
As a precaution until they are patched, after the flaws were disclosed (The Irish Times, 2026; Deccan Chronicle, 2026).
References
- Deccan Chronicle (2026) Govt Websites Go Dark After AI-Discovered Flaw Sparks Security Scramble. Deccan Chronicle. Available at: Govt Websites Go Dark After AI-Discovered Flaw (Accessed: 22 October 2026).
- Gulf News (2026) PHP fixes two critical vulnerabilities as websites face attack risks. Gulf News. Available at: PHP fixes two critical vulnerabilities (Accessed: 22 October 2026).
- Inc42 (2026) Inside Critical PHP Vulnerabilities That Have 70% Of The Internet At Risk. Inc42. Available at: Inside Critical PHP Vulnerabilities (Accessed: 22 October 2026).
- The Irish Times (2026) 'Critical vulnerabilities' found in computer code supporting up to 70% of internet. The Irish Times. Available at: Critical vulnerabilities found in computer code (Accessed: 22 October 2026).
How we did this
On 22 October 2026 we read the PHP patch details reported by Gulf News, which cite the UK NCSC and the PHP security team, and Inc42's technical breakdown, and set the fixed versions against what agencies advise. We took the government outages and scale figures from The Irish Times and Deccan Chronicle, and searched for Indian sites that went offline but found none named. We could not open CERT-In's advisory. The hero image is a flow chart we drew from the reported dates; upload it with the story.
This story was produced, reviewed, edited and verified by the reporter before publication, with AI assistance where required.
Covered by 33 outlets across the spectrum: 15% left, 39% center, 45% right.
Who is covering this story
- Left-leaning (5): The Verge, NDTV, Daily Mirror, The Irish Times, The New Indian Express
- Center (9): Hindustan Times, Tribune India, Financial Times, The Hindu BusinessLine, Abc7 News, Global News, Inc42, EIN Presswire, The Star (Reuters)
- Right-leaning (6): Usnews, Sunday Guardian, Gulf News, Times of India, Times Now, Deccan Chronicle
Sources
- Cyber Agency Warns Websites May Go Dark as PHP Prepares Critical Fix — Usnews (right-leaning, AI-estimated) ·
- A critical programming vulnerability may take websites down today — The Verge (left-leaning, AI-estimated) ·
- PHP Security Alert: Two Critical 9.2-Rated Vulnerabilities Threaten Website Security; EU Agency Warns of Possible Shutdowns — Check Affected Systems, Emergency Patches & Safety Tips — Sunday Guardian (right-leaning) ·
- PHP fixes two critical vulnerabilities as websites face attack risk — Gulf News (right-leaning) ·
- Govts in Europe take down sites, US urges fix after AI discovers flaw in programming language PHP — Hindustan Times (center) ·
- Decades-old flaw discovered in PHP forces govt websites to go offline globally — Times of India (right-leaning) ·
- Government websites in Europe, elsewhere go dark after AI-discovered flaw sparks security scramble — Tribune India (center) ·
- What Is PHP Software? Critical Security Flaw Forces Government Websites To Shut Down — Times Now (right-leaning) ·
- Japan PM, FBI Warn of Critical PHP Security Flaws as Major Websites Go Offline — Deccan Chronicle (right-leaning) ·
- PHP Vulnerability Explained: Who Is At Risk, How To Fix, What WordPress Users Should Know — NDTV (left-leaning) ·
- Websites taken offline in race to patch PHP security flaw — Financial Times (center) ·
- Govt Warns PHP Security Flaws Could Let Hackers Take Control Of Websites: What To Know — Times Now (right-leaning) ·
- What Is PHP and Why Are Its Newly Discovered Security Flaws Raising Fears of Data Theft, Server Takeovers and Cyberattacks Worldwide? — Sunday Guardian (right-leaning) ·
- PHP security flaws trigger millions of exploit attempts, says Cloudflare CEO — The Hindu BusinessLine (center) ·
- PHP security flaws put 70% of the internet at risk, says Wiz — The Hindu BusinessLine (center) ·
- PHP Issue Explained: Why Millions Of Websites Are Going Dark Globally — Times Now (right-leaning) ·
- Cybersecurity expert warns situation is 'serious' as 'millions of sites impacted by PHP vulnerabilities' — Daily Mirror (left-leaning) ·
- PHP vulnerability 2026: Websites shut down globally as operators address AI-detected flaw in web programming language — Abc7 News (center, AI-estimated) ·
- Statistics Canada website down as internet hit by millions of hack attempts — Global News (center, AI-estimated) ·
- ‘Critical vulnerabilities’ found in computer code supporting up to 70% of internet — The Irish Times (left-leaning) ·
- Govt Websites Go Dark After AI-Discovered Flaw Sparks Security Scramble — Deccan Chronicle (right-leaning) ·
- Inside PHP Vulnerabilities That Have 70% Of The Internet At Risk — Inc42 (center) ·
- Websites across Europe taken down as PHP flaws spark alarm — Gulf News (right-leaning) ·
- One flaw, millions of websites : The PHP2Shell threat — The Hindu BusinessLine (center) ·
- PHP flaws spark global alarm, Indian firms scramble to patch systems — The Hindu BusinessLine (center) ·
- PHP vulnerabilities explained: How two security flaws could expose millions of websites — The Hindu BusinessLine (center) ·
- Dow Digital Announces Emergency Defense and Patching Services for Core PHP Vulnerabilities — EIN Presswire (center, AI-estimated) ·
- From Japan To Kenya, PHP Security Flaw Disrupts Websites Worldwide — Times Now (right-leaning) ·
- PHP security flaws trigger global scramble; CERT-In flags vulnerabilities — Times of India (right-leaning) ·
- Websites down: what is PHP and how has it raised AI hacking fears? — The Star (Reuters) (center) ·
- DC Edit | PHP Flaws, AI Prying Point At Need For Digital Security — Deccan Chronicle (right-leaning) ·
- Two critical PHP flaws trigger global alert; millions of services face cyber risk — Times of India (right-leaning) ·
- Patched PHP flaws in 10 govt sites, two others being fixed, says IT secy — The New Indian Express (left-leaning) ·